The system that keeps business working
Engineering the systems, operations and critical environments your business depends on.
TRILOGY designs and implements infrastructure, protection, recovery and operational solutions — shaped around your requirement, not around a fixed package.
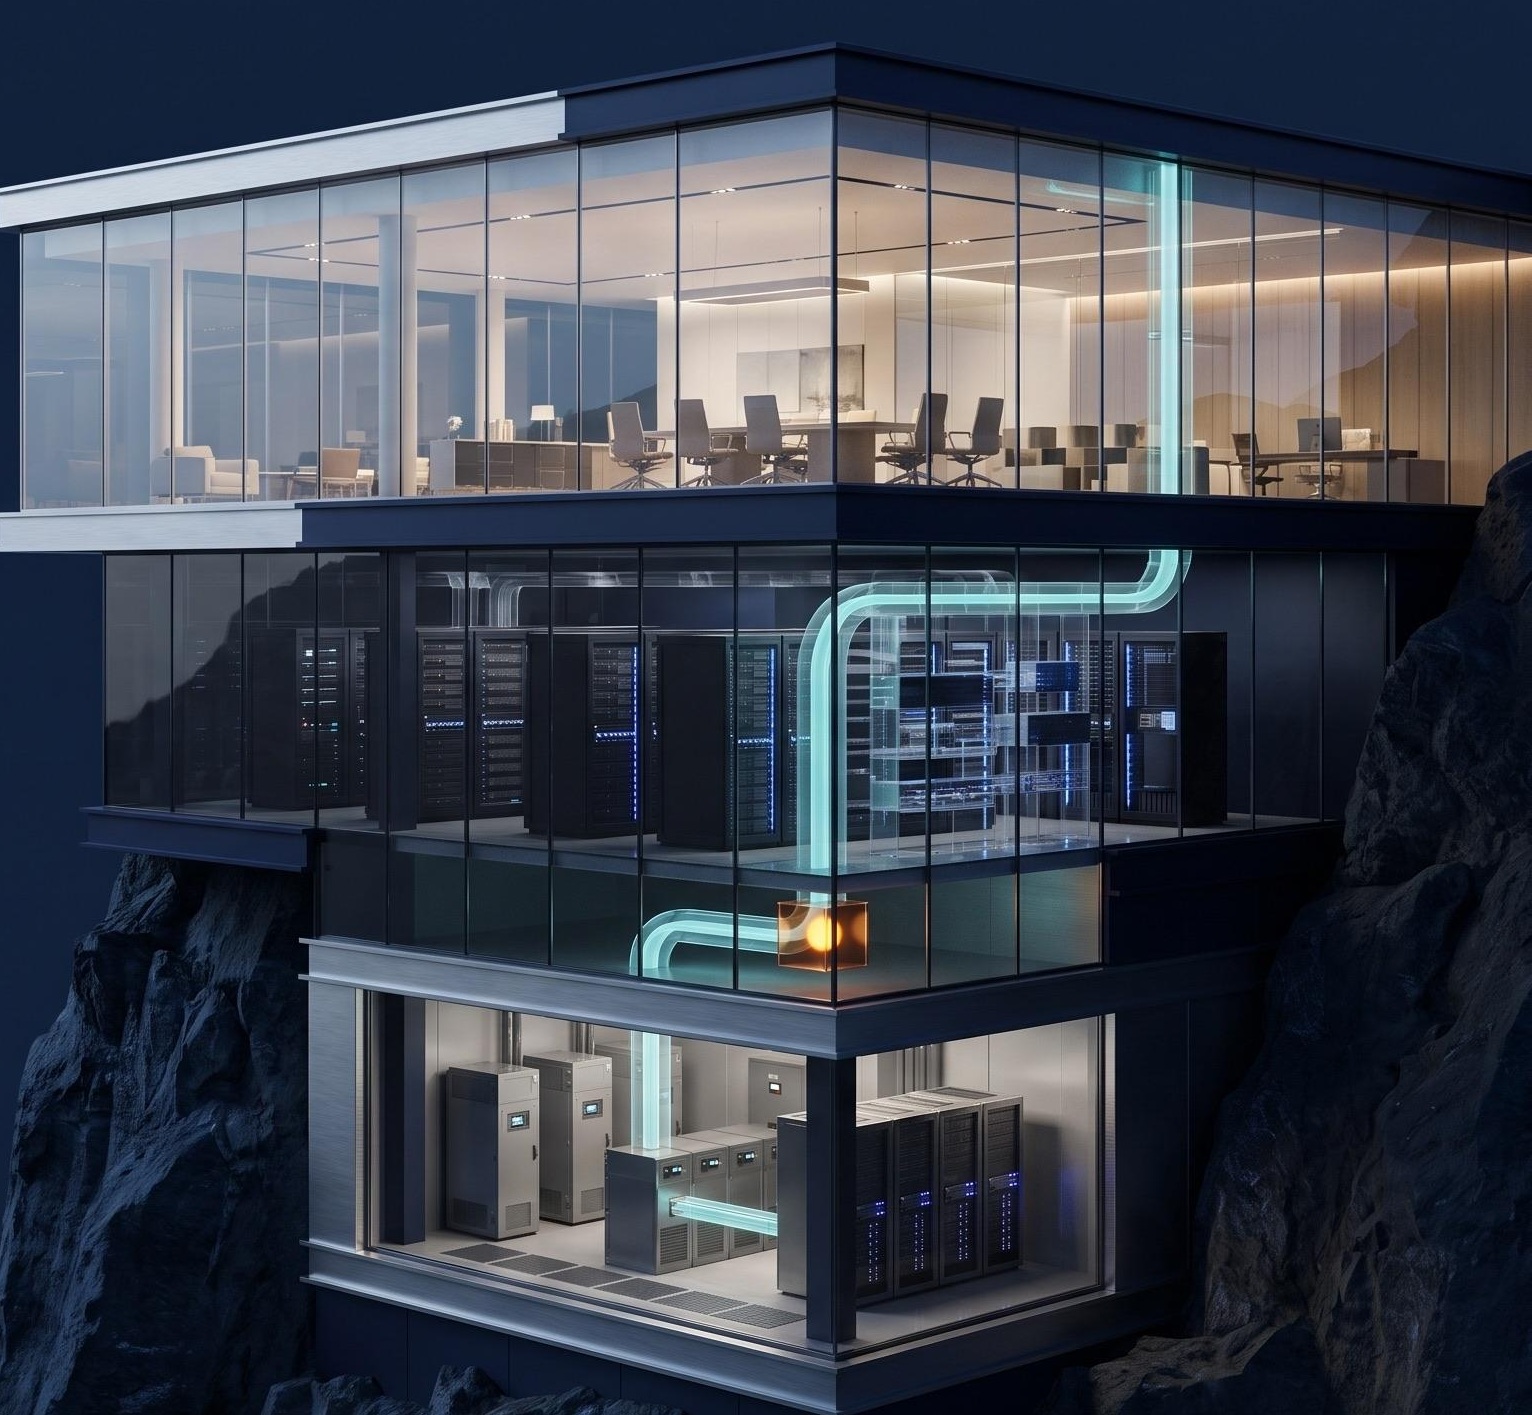
- Business service↓ depends on
- Identity · Data · Applications↓ depends on
- Physical infrastructure
Choose your starting point
Start from where your requirement actually is.
A defined RFQ does not need an assessment first. Pick the closest description and see how the first conversation works.
A defined project or RFQ
Share the RFQ detailsFour solution worlds
One accountable partner across the layers your services depend on.
01
Infrastructure & Cloud
Capacity that matches demand, without fragile hand-offs between data centre and cloud.
How it works: Compute, storage and network designed as one architecture, with placement decided per workload.
Who it's for: Where should each workload run, and on what?
Capabilities in this world
- Enterprise & Object Storage
- Compute, Virtualisation & HCI
- AI & HPC Infrastructure
- Edge & IoT Infrastructure
- Data Centre Facilities & Operations
- Hybrid & Private Cloud
- Cloud Landing Zones & Microsoft 365
What we cover
Design
Workload and capacity map, platform selection, architecture, power and cooling.
Implementation
Installation, configuration, migration with rollback, lifecycle baseline.
Verification & handover
Failover, performance and acceptance tests.
02
Networking & Digital Workspace
Networks and workspaces that connect people to services, safely.
How it works: Campus, branch, data-centre fabrics, remote access, virtual desktops and voice — designed as one path with clear access boundaries.
Who it's for: Can users and sites connect reliably and securely?
Capabilities in this world
What we cover
Design
Topology, addressing, segmentation, workspace personas.
Implementation
Switching, wireless, fabrics, SAN, VDI, voice.
Verification & handover
Acceptance tests, failover, pilot users.
03
Cybersecurity
Controls that reduce exposure and that your team can operate day to day.
How it works: Identity, endpoint and network controls layered around what you need to protect.
Who it's for: Who and what can reach the service, under which control?
Capabilities in this world
- Next-Generation Firewalls & Segmentation
- Endpoint Protection, EDR & XDR
- Privileged Access Management
- NAC & Zero Trust Network Access
- Email & Collaboration Security
- Data Protection & DLP
- WAF, API Protection & DDoS
- Network Detection & Response
- OT, IoT & Cyber-Physical Security
What we cover
Design
Control architecture per layer, policy design, phased enforcement.
Implementation
Platform deployment, integration with identity and logging, migration from legacy tools.
Verification & handover
Policy tests, retest of findings, exception and remediation register.
04
Backup & Recovery
Confidence that critical services can be brought back — and evidence of how.
How it works: Protected, isolated copies with a recovery path that is tested, not assumed.
Who it's for: Can the service come back, and has it been proven?
Capabilities in this world
What we cover
Design
Coverage review, recovery tiers per service, retention and immutability, isolated recovery design.
Implementation
Backup platform, repositories and vaults, replication for critical apps, Microsoft 365 and SaaS coverage, monitoring.
Verification & handover
Restore tests per service, DR drill, exceptions and improvement plan.


Digit — TRILOGY's ERP for finance, sales, purchasing, inventory and point of sale.
Cybersecurity
Security controls, designed, deployed and tuned for your environment.
NGFW / NDR / Network Analytics
- App/user-aware NGFW policies
- East-west visibility
- Encrypted traffic analytics
Endpoint Protection & XDR
- Behavioural AI / EDR
- Rollback & containment
- Unified telemetry across assets
PAM / Identity Security
- SSO/MFA federation
- Privileged session management
- Just-in-time access
Email Security / Threat Protection
- BEC & phishing defence
- Impersonation protection
- Sandboxing & malware removal
SSE / ZTNA / Cloud SWG / NAC
- ZTNA with MFA & posture
- Cloud SWG & CASB controls
- NAC & micro-segmentation
OT/IoT Security
- Asset & protocol discovery
- Network segmentation
- Threat detection for OT/IoT
WAF / App & API + DDoS
- API discovery & protection
- Bot & DDoS mitigation
- Runtime WAAP policies
Data Protection & DLP
- Sensitive data discovery
- Policy-based DLP
- Audit & reporting
Bespoke cyber engineering
From the network edge to endpoints and email, we build security that fits your business. Our architects model risk and throughput; our engineers plan controlled cutovers; our team keeps the stack tuned as threats evolve.
- Architecture & sizing workshops
- HA / SD-WAN rollouts & segmentation
- Identity, SSO & SAML integrations
- Logging, SIEM/SOAR automation & MDR options
Built for Saudi requirements. Delivered by TRILOGY.
We design, deploy and operate security controls that support your NCA ECC, SAMA CSF, DGA and NDMO obligations — mapped to your scope and classification.
From requirement to handover
A delivery path you can follow and review.
If your requirement is already defined, we start at architecture — no mandatory assessment.
- 1
Requirement
Agree what must be true when the work is done.
- 2
Architecture
Design the solution and state its assumptions.
- 3
Change
Implement through a planned, approved change.
- 4
Verification
CheckpointTest against the agreed requirement.
- 5
Evidence
Record results and open exceptions.
- 6
Handover
Transfer documentation and operating knowledge.
Data centre technologies
Use only what you need — combine one or more technologies into a solution sized for your workload.
Storage & Data
Unify block, file and object with NVMe-oF performance, snapshots/replication and ransomware-ready immutability across hybrid cloud.
- Unified block/file/object
- NVMe-oF + replication
- Immutability & tiering
Compute, Virtualisation & HCI
x86 and composable platforms with HCI and virtualisation, policy-based profiles, lifecycle automation and ROBO/edge options.
- PCIe Gen5 + GPUs
- HCI & dHCI
- Composable templates
Edge & IoT
Rugged edge compute, gateways and fleet management for secure OT/IT convergence with local analytics.
- Rugged servers/gateways
- Secure OT/IT
- Fleet management
AI & HPC
Validated NVIDIA stacks and HPC platforms with RDMA/NFS pipelines, from POC to cluster, with liquid-cooling options.
- OVX/HGX validated
- NFS over RDMA
- Cluster-ready
Operations, Control Plane & DC Infra
Out-of-band and lifecycle automation, data-centre management, UPS and liquid cooling for dense workloads.
- Automation/API
- OOB & telemetry
- UPS & liquid cooling
Networking & Connectivity
DC fabrics (VXLAN/EVPN), Fibre Channel SAN and 10–800G optics for AI-ready infrastructure.
- VXLAN/EVPN fabrics
- 16/32/64G FC SAN
- QSFP-DD / OSFP 800G
Infrastructure
Hybrid infrastructure stack
Automated lifecycle, resilient high availability and consistent hybrid operations.
- Policy-driven lifecycle management
- Stretched HA & micro-segmentation
- Unified observability
Workspace capabilities
Digital workspace & ops
Secure, elastic desktops and apps for hybrid work — VDI/DaaS with stable profiles, optimised calls and day-2 automation.
Azure Virtual Desktop (AVD)
Elastic Windows desktops with Conditional Access & FSLogix.
- · Autoscale
- · MSIX app attach
- · Teams optimisation
Citrix DaaS
Cloud-managed delivery of apps & desktops.
- · Global control plane
- · Autoscale
- · Hybrid connectors
Citrix Virtual Apps & Desktops (LTSR/CR)
Enterprise brokering with HDX experience.
- · HDX
- · Image rings
- · App layering
Image & Provisioning (PVS)
Golden images streamed at scale with rollback.
- · vDisk streaming
- · Versioning
- · Rapid patch waves
Recovery mechanism
Which critical service have you proven you can restore?
A recovery plan must account for identity, data, applications and infrastructure—not only the backup job. Define the service, design the recovery path and verify it under agreed test conditions.
Cyber resilience
Immutable, isolated copies and clean-room recovery
Recover at speed
Orchestrated, tested recovery runbooks
Any workload, any cloud
VMs, physical servers, databases, Kubernetes, Microsoft 365 / SaaS and object storage
Platforms and workloads we protect
- VMware vSphere
- Hyper-V
- Nutanix AHV
- Kubernetes / OpenShift
- Oracle
- SQL Server
- SAP HANA
- Microsoft 365
- Salesforce
- Entra ID / AD
- AWS
- Azure
- Google Cloud
- OCI
- S3-compatible object storage
- NAS
- Windows / Linux servers

01
Protected copy
An immutable copy held apart from production.
02
Isolated recovery environment
Data is validated before it returns.
03
Business service restored
The service runs again on verified data.
Illustration of the recovery mechanism — not a customer test result.
Control and evidence
Technology that works—and leaves evidence.
Connect your cybersecurity requirement to a defined technical scope, implementation and verification. Start with your current architecture, a technical finding or an RFQ; an assessment is not mandatory for every request.
Illustrative deliverable types — not customer records.

DOC-01
Scope document
Objectives, boundaries, assumptions
DOC-02
Change plan
Steps, windows, rollback
DOC-03
Test record
Test cases and results
DOC-04
Exceptions register
Open items and owners
DOC-05
Handover documentation
As-built, runbooks, contacts
Professional services
Managed, project-based and cloud services to operate securely at scale.
Technologies we design and implement
Names and trademarks belong to their owners.
Discuss your requirement
What are you working on now?
Share the requirement, RFQ, renewal or technical finding you want to discuss. Include the affected systems and any constraints you already know.